

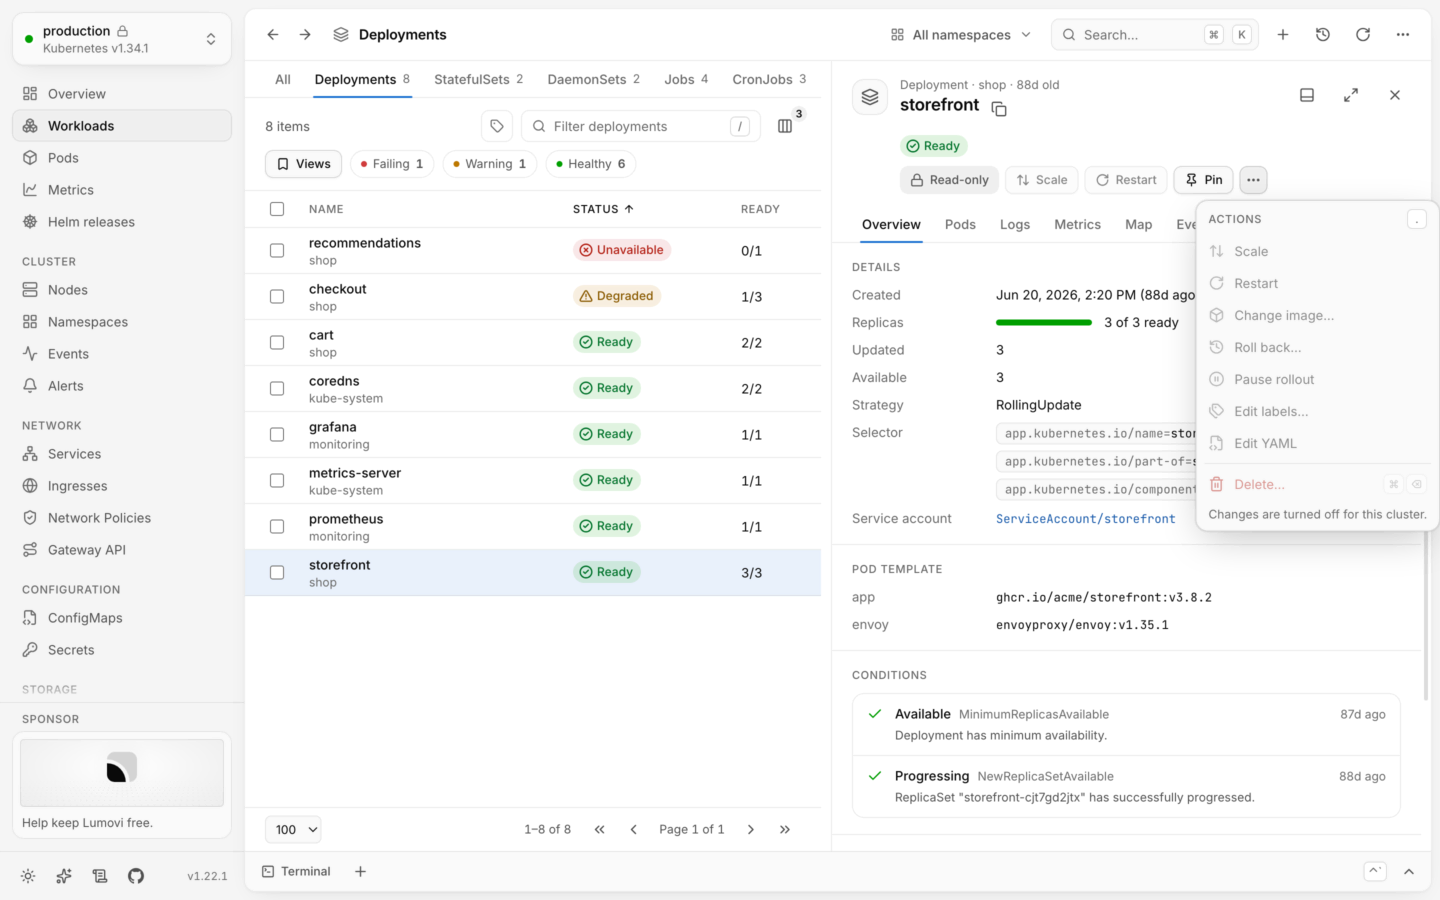

A cluster made read-only: Lumovi won't change anything in it until allowed.
For one cluster
- Cluster switcher
- Command palette
Open the cluster switcher at the top of the sidebar, and turn on Read-only. Its caption reads “Lumovi won’t change” and the cluster’s name.
For every cluster
SetLUMOVI_READ_ONLY to 1 (or true) in the environment Lumovi starts in. Every cluster is read-only, and it can’t be turned off from the app: the switch is disabled, with the caption “Set by LUMOVI_READ_ONLY”, and the command palette leaves out its read-only command. That makes it a good fit for shared machines, demos and screen shares.
Set by your organization
Your organization’s policy can make every cluster read-only on its computers, or those whose names match, likeprod-*. You can’t turn it off for those: the switch is disabled, with the caption “Set by your organization”, the command palette leaves out the read-only command, and the Read-only badge says “Your organization’s policy makes production read-only.”, without Allow changes. You can still make other clusters read-only yourself.
A policy that can’t be used makes every cluster read-only until it’s put right, and the badge says why: “Lumovi can’t use your organization’s policy (…), so it changes no cluster until it’s put right.”
What it turns off
It isn’t only the buttons. The part of Lumovi that talks to your clusters (the desktop app’s main process, or the server when Lumovi runs in your cluster) refuses every change to a read-only cluster, whatever asks for it:production is read-only in Lumovi. Allow changes to it to continue.On a server, it says who made it read-only, and when: see In your cluster.
Actions that are off stay visible, disabled, with “Changes are turned off for this cluster.” (on a server, with who made it so). One button stays enabled: Install chart on Helm releases. Its dialog opens, and when you choose Review, it shows the refusal above instead of a dry run.
A shell’s tab, in a pod or on a node, says Shells are off instead of opening one.
AI assistants still read a read-only cluster, but can’t change it. On the Permissions tab of the AI assistants page, Check a namespace says its changes are Never: read-only, whatever the rules say, and
list_clusters tells assistants it’s read-only. A change one asks for anyway is refused before you’re asked, and the assistant gets the message above.
Terminals aren’t covered
The read-only switch doesn’t apply to the desktop app’s terminals. A terminal is your own shell on your computer, with your own credentials. kubectl and helm there do whatever your account allows, as in any other terminal, whether Lumovi has the cluster read-only or not. A terminal started for a read-only cluster says so: “Lumovi’s read-only switch doesn’t apply to what you run here.”In your cluster
When Lumovi runs in your cluster, or as a fleet, read-only is the server’s, the same for everyone on it, and their AI assistants:- For one cluster. The cluster switcher’s Read-only reads “Lumovi won’t change production for anyone on this server”. Turned on, it says who did, and when: “Turned on by jane@example.com, Oct 7, 2026, 2:20 PM”. It’s on for everyone, and stays on until it’s turned off, by anyone who may.
- Who may. Lumovi’s admins (
access.admins,LUMOVI_ADMINS), or, where it has none, anyone signed in. For everyone else, the switch is disabled, with “Only Lumovi’s admins change it”, and the Read-only badge says “Only Lumovi’s admins change what’s set for everyone on this server.” instead of Allow changes. The command palette offers Make cluster read-only, and Allow changes to cluster, only to those who may. - For every cluster. Set
readOnly: truein the Helm chart’s values (LUMOVI_READ_ONLY=truewhen you run the image another way). Nobody changes anything through Lumovi, whatever their RBAC allows, and neither do their AI assistants. The switch shows “For everyone, on this server”, and nobody can turn it off on the page. See Helm values.
- The Read-only badge: “Changes are off for production”, then “jane@example.com made it read-only for everyone on this server on Oct 7, 2026, 2:20 PM. Lumovi won’t change anything in it for anyone until it’s allowed again.”, with Allow changes for those who may.
- Actions and dialogs: “Changes are turned off for this cluster: jane@example.com made it read-only for everyone.”
- Shells: “jane@example.com made production read-only for everyone on this server, and a shell can change a container.” (on a node, “…and a node shell can change the node.”)
- What the server refuses, a change, a Helm action, a shell, or an AI assistant’s change: “production is read-only for everyone on this server: jane@example.com made it so.”
- Made read-only outside Lumovi, by an older copy put back, none of them names anyone: the switch says “Turned on outside Lumovi”, the badge “It was made read-only for everyone on this server outside Lumovi. Lumovi won’t change anything in it for anyone until it’s allowed again.”, actions “Changes are turned off for this cluster: it was made read-only for everyone outside Lumovi.”, shells “production was made read-only for everyone on this server outside Lumovi, and a shell can change a container.”, and the server “production is read-only for everyone on this server: it was made so outside Lumovi.”
read-only.changed: “Made production read-only for everyone on this server”, or “Made production changeable for everyone on this server”. So is each attempt by someone who may not, as refused.
It’s kept where the server keeps what a restart mustn’t lose: the Secret the chart makes (auth.keepSessions, on by default), or LUMOVI_DATA_DIR. Without either, it’s in memory: a restart turns it off, and each replica would have its own, so run one. Lumovi’s log says so as it starts, and the chart refuses more than one replica without auth.keepSessions. Kept, with more than one replica, a change reaches the others within 10 seconds, and open pages show it as soon as their server has it. See Across restarts.
It’s kept by the cluster’s name, as Lumovi lists it: a cluster renamed doesn’t keep what was set for it.
Changed outside Lumovi
Whoever can write where the server keeps it, the Secret orstate.json, can’t make an entry without its key (kept apart from it), but could delete a cluster’s setting, or put an older copy of it back: its read-only off, say, or its node shells as they once were. So each of a cluster’s settings carries the count of the write that last set it, and Lumovi never sets one lower than it was. As Lumovi reads them again, every 10 seconds, a setting gone, or counting lower than what it knew, was changed outside Lumovi. Lumovi keeps each setting as whichever copy set it last, failing closed:
- Read-only, if either has it. Turned off that way, Lumovi makes it read-only again, as whoever made it so had it. Made read-only by an older copy, it stays so, and Lumovi says it was made so outside Lumovi, naming nobody.
- Its metrics source and node shells as Lumovi last set them, never an older copy’s.
- In the audit log, by Lumovi itself, with
outside: true: asread-only.changed, “Changed outside Lumovi: production’s read-only was turned off, as its setting was deleted where Lumovi keeps it, and Lumovi made it read-only again”, or “Changed outside Lumovi: production was made read-only for everyone, as an older copy of its setting was put back where Lumovi keeps it”; asnode-shell.changed, “Changed outside Lumovi: production’s node shells were changed, as an older copy of its setting was put back where Lumovi keeps it, and Lumovi put back what it last set”; and asmetrics-source.changed, “Changed outside Lumovi: production’s metrics source was changed, as …, and Lumovi put back what it last set”. It’s recorded by the first replica to find it, or by the change an admin makes over it, which fixes it first; and again by a replica that knew newer settings than that one did. The audit event names the copy found by its count (found), where Lumovi can tell. - In Lumovi’s log:
What’s set for production was changed outside Lumovi: its setting was deleted where Lumovi keeps it. Lumovi kept the stricter (read-only again), and it’s recorded in the audit log.A change that leaves all Lumovi sets as it was is only in the log:What’s set for production was changed outside Lumovi (…), but nothing it sets. - To Lumovi’s admins (anyone signed in, where it has none), on the cluster’s pages, on every replica: “production’s read-only was turned off outside Lumovi, and Lumovi made it read-only again.”, “production was made read-only outside Lumovi.”, or “What’s set for production was changed outside Lumovi, and Lumovi put it back.”, then, like, “On Oct 7, 2026, 2:20 PM, an older copy of its setting was put back where Lumovi keeps it, by whoever can write there. Lumovi put back its node shells as it last set them. It’s in the audit log.” (“…its metrics source as it last set it.”, or “…its metrics source and node shells as it last set them.”) Its buttons follow what the cluster is now: read-only, Keep it read-only and Allow changes; changeable, Keep it changeable and Make it read-only. Either is their own change, recorded as theirs: Keep it read-only names them as who made it read-only. The banner stays until read-only is set again, with either button, the switch, or the command palette: a change to the cluster’s metrics source or node shells leaves it.
- A change made while no replica runs, as while an upgrade stops the old pod before starting the new one, is taken as found: a replica that starts knows nothing older. An older copy put back after that, while one runs, is still found: what Lumovi writes next counts above it. What that copy set, and the entry made again didn’t, is put back as Lumovi last set it, and recorded; its read-only stays on, as made outside Lumovi. But if a replica that never read the entry made again writes over that copy first, the copy’s settings stay, unrecorded.
- A replica that’s behind, briefly. A replica that hadn’t yet read the latest time read-only was turned on can take a copy from before then, in which an admin had turned it off, for Lumovi’s own. A replica that read it turns it back on at its next read, within 10 seconds.
- Clocks. Two writes of the same setting, by replicas that didn’t see each other’s, one of them over a copy put back, come out by their clocks: a replica whose clock is behind loses to an older copy written by one whose clock is right, and so does one writing in the same millisecond. Keep the nodes’ clocks in sync.
- A setting copied from another install with the same key, counting higher, passes as Lumovi’s own: give each install its own key. See Across restarts.
Read-only mode is a guard rail in Lumovi, not a permission. To keep someone from changing a cluster at all, give their account read-only RBAC, like the built-in
view ClusterRole. See Permissions.Changing things safely
The other guard rails, for when changes are on.
Environment variables
Everything Lumovi reads from its environment.